Readings Newsletter
Become a Readings Member to make your shopping experience even easier.
Sign in or sign up for free!
You’re not far away from qualifying for FREE standard shipping within Australia
You’ve qualified for FREE standard shipping within Australia
The cart is loading…
This title is printed to order. This book may have been self-published. If so, we cannot guarantee the quality of the content. In the main most books will have gone through the editing process however some may not. We therefore suggest that you be aware of this before ordering this book. If in doubt check either the author or publisher’s details as we are unable to accept any returns unless they are faulty. Please contact us if you have any questions.
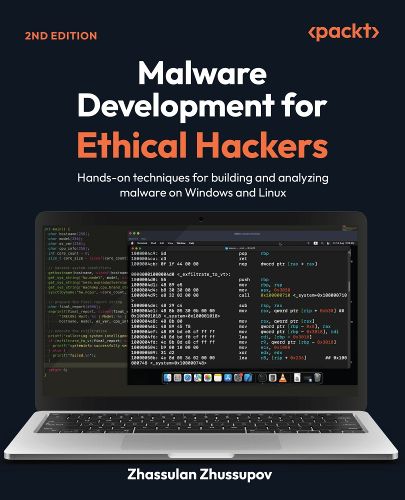
Expanded to cover malware development across Windows and Linux, persistence, injection, evasion, and malware analysis, this practical, lab-based guide uses real-world examples to equip ethical hackers with hands-on skills.
Key Features
Build practical malware PoCs using C/C++ and Assembly in controlled labs Apply red and blue team perspectives to understand malware behavior, detection opportunities, and forensic artifacts Explore execution, injection, persistence, evasion, and anti-analysis techniques Purchase of the print or Kindle book includes a free PDF eBook
Book DescriptionMalware Development for Ethical Hackers, Second Edition is a practical guide to understanding how modern malware works across Windows and Linux in an ethical, research-driven context. It focuses on controlled proof-of-concept development, showing how adversaries build capabilities such as droppers, keyloggers, infostealers, loaders, persistence modules, and process injection techniques. The second edition covers malware development for Windows and Linux, with hands-on examples in C/C++ and Assembly. You'll explore execution techniques, evasion, persistence, anti-analysis, abuse of legitimate APIs, low-level system techniques, and real-world tradecraft inspired by modern APTs and malware families. The book also connects offensive development with malware analysis, detection opportunities, and forensic artifacts for security researchers and Blue Team readers. By the end of this book, you'll understand how malware is designed, executed, hidden, persisted, and analyzed across Windows and Linux. You'll be able to build safe lab PoCs, understand adversary behavior, recognize forensic artifacts, and apply this knowledge to ethical hacking, red team simulations, malware research, and practical defense.What you will learn
Implement execution and injection techniques across Windows and Linux Explore persistence mechanisms and the artifacts they leave behind Develop practical PoCs for droppers, keyloggers, infostealers, and loaders Study evasion, anti-analysis, and living-off-the-land techniques to understand how malware avoids detection Reconstruct real-world adversary tradecraft for red team simulations, security research, and defensive improvement
Who this book is forThis book is for penetration testers, red team engineers, malware researchers, exploit developers, threat hunters, and blue team analysts who want to understand how real-world malware techniques work in practice. It is also useful for ethical hackers and cybersecurity students seeking hands-on experience with malware concepts across Windows, Linux, macOS, Android, and iOS in controlled lab environments. Familiarity with C/C++, basic Assembly, operating system internals, and core cybersecurity concepts will help readers get the most from the examples.
$9.00 standard shipping within Australia
FREE standard shipping within Australia for orders over $100.00
Express & International shipping calculated at checkout
Stock availability can be subject to change without notice. We recommend calling the shop or contacting our online team to check availability of low stock items. Please see our Shopping Online page for more details.
This title is printed to order. This book may have been self-published. If so, we cannot guarantee the quality of the content. In the main most books will have gone through the editing process however some may not. We therefore suggest that you be aware of this before ordering this book. If in doubt check either the author or publisher’s details as we are unable to accept any returns unless they are faulty. Please contact us if you have any questions.
Expanded to cover malware development across Windows and Linux, persistence, injection, evasion, and malware analysis, this practical, lab-based guide uses real-world examples to equip ethical hackers with hands-on skills.
Key Features
Build practical malware PoCs using C/C++ and Assembly in controlled labs Apply red and blue team perspectives to understand malware behavior, detection opportunities, and forensic artifacts Explore execution, injection, persistence, evasion, and anti-analysis techniques Purchase of the print or Kindle book includes a free PDF eBook
Book DescriptionMalware Development for Ethical Hackers, Second Edition is a practical guide to understanding how modern malware works across Windows and Linux in an ethical, research-driven context. It focuses on controlled proof-of-concept development, showing how adversaries build capabilities such as droppers, keyloggers, infostealers, loaders, persistence modules, and process injection techniques. The second edition covers malware development for Windows and Linux, with hands-on examples in C/C++ and Assembly. You'll explore execution techniques, evasion, persistence, anti-analysis, abuse of legitimate APIs, low-level system techniques, and real-world tradecraft inspired by modern APTs and malware families. The book also connects offensive development with malware analysis, detection opportunities, and forensic artifacts for security researchers and Blue Team readers. By the end of this book, you'll understand how malware is designed, executed, hidden, persisted, and analyzed across Windows and Linux. You'll be able to build safe lab PoCs, understand adversary behavior, recognize forensic artifacts, and apply this knowledge to ethical hacking, red team simulations, malware research, and practical defense.What you will learn
Implement execution and injection techniques across Windows and Linux Explore persistence mechanisms and the artifacts they leave behind Develop practical PoCs for droppers, keyloggers, infostealers, and loaders Study evasion, anti-analysis, and living-off-the-land techniques to understand how malware avoids detection Reconstruct real-world adversary tradecraft for red team simulations, security research, and defensive improvement
Who this book is forThis book is for penetration testers, red team engineers, malware researchers, exploit developers, threat hunters, and blue team analysts who want to understand how real-world malware techniques work in practice. It is also useful for ethical hackers and cybersecurity students seeking hands-on experience with malware concepts across Windows, Linux, macOS, Android, and iOS in controlled lab environments. Familiarity with C/C++, basic Assembly, operating system internals, and core cybersecurity concepts will help readers get the most from the examples.
Search our extensive online catalogue.